Name resulution of AAD Groups is iffy

Hello there,

i think i have a weird issue with the name resolution of AAD groups in my ACL or generaly in TrueNAS.

Lets start with some Context:

I Run a Proxmox Instance that is up to date and in there i run the VM for TrueNAS Community Edition. Here is a little Overview:
Not much goining on atm.

I am connected to my onprem DC:
The OnPrem DC ist connectted with a AD-Sync to my AAD (Azure Active Directory) [now its called Entra ID] to sync down the Cloud groups to my DC.

My DC has all the groups of my AAD.

If i go to the Shell of the Truenas instance i can:

"getent group” and get all the groups from Truenas and also the local groups that exist in my OnPrem DC. I DO NOT GET ANY AAD GROUP :frowning:

but…

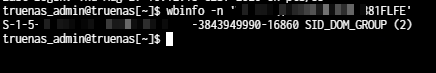
Now here is a funny thing with the matching of AAD groups and if they get synced down to a onprem DC. They do not get their normal Displayname, they will be only found from my TrueNAS Instance with their sAMAccountName:
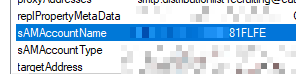
image

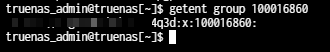
This actually worked like it should:

image

Matching to the RID also fine:

image

Now even tho its not pretty my guess was i can just match the ACL groups with the sAMAccountName and be done with the permissions.

But:
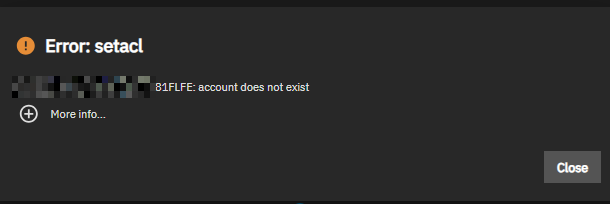
Now i know i am not using the latest TrueNAS version. And its a step that i should make. Before that i would one kind soul to explain to me the problem i am havin right now, if possible.

AD.adv.Settings:
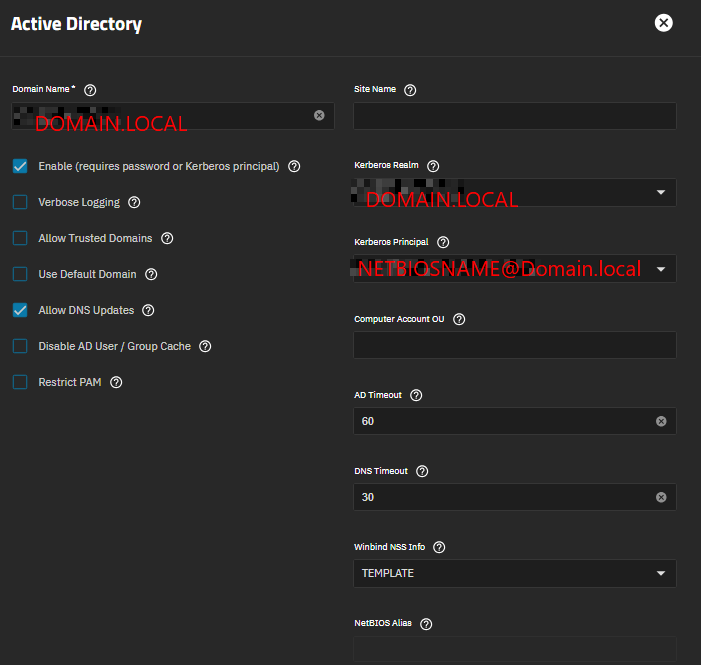
lmao found the issue.

The AAD/Entra groups are actually synced correctly and are resolved correctly by Winbind/TrueNAS. The problem seems to be a case-sensitive group lookup when setting the ACL.

For example, the group is returned from AD like:

DOMAIN\$GENERATEDGROUPNAME

Basic resolution works:

wbinfo -n 'DOMAIN\$GENERATEDGROUPNAME'
getent group 'DOMAIN\$GENERATEDGROUPNAME'

and TrueNAS itself can resolve both the name and GID:

midclt call group.get_group_obj '{"groupname":"DOMAIN\\$GENERATEDGROUPNAME","sid_info":true}'

midclt call group.get_group_obj '{"gid":<GID>,"sid_info":true}'

However, TrueNAS/Winbind returns the canonical group name in lowercase:

DOMAIN\$generatedgroupname

This reproduces the issue:

# uppercase / original name - fails
midclt call group.query '[["group","=","DOMAIN\\$GENERATEDGROUPNAME"]]' '{"get":true}'

# lowercase canonical name - works
midclt call group.query '[["group","=","DOMAIN\\$generatedgroupname"]]' '{"get":true}'

# case-insensitive lookup - also works
midclt call group.query '[["group","C=","DOMAIN\\$GENERATEDGROUPNAME"]]' '{"get":true}'

So the AAD group itself is fine. The problem is that the ACL lookup appears to use a case-sensitive group query.

Workaround: use the lowercase/canonical group name returned by TrueNAS:

DOMAIN\$generatedgroupname

After using that name, the ACL can be saved successfully.

So this appears to be a TrueNAS case-sensitivity issue rather than an AAD/AD synchronization problem.

Makes sense. I’ve seen a similar thing when entering AD groups in TrueNAS doesn’t seem to like uppercase.

cache UI / API queries against is generated against names normalized by nss_winbind. Lower layer than truenas middleware. Consistent name normalization at OS level is important for various security-adjacent reasons.