S_R
August 20, 2025, 1:02am
1
raise SMTPResponseException(code, message)
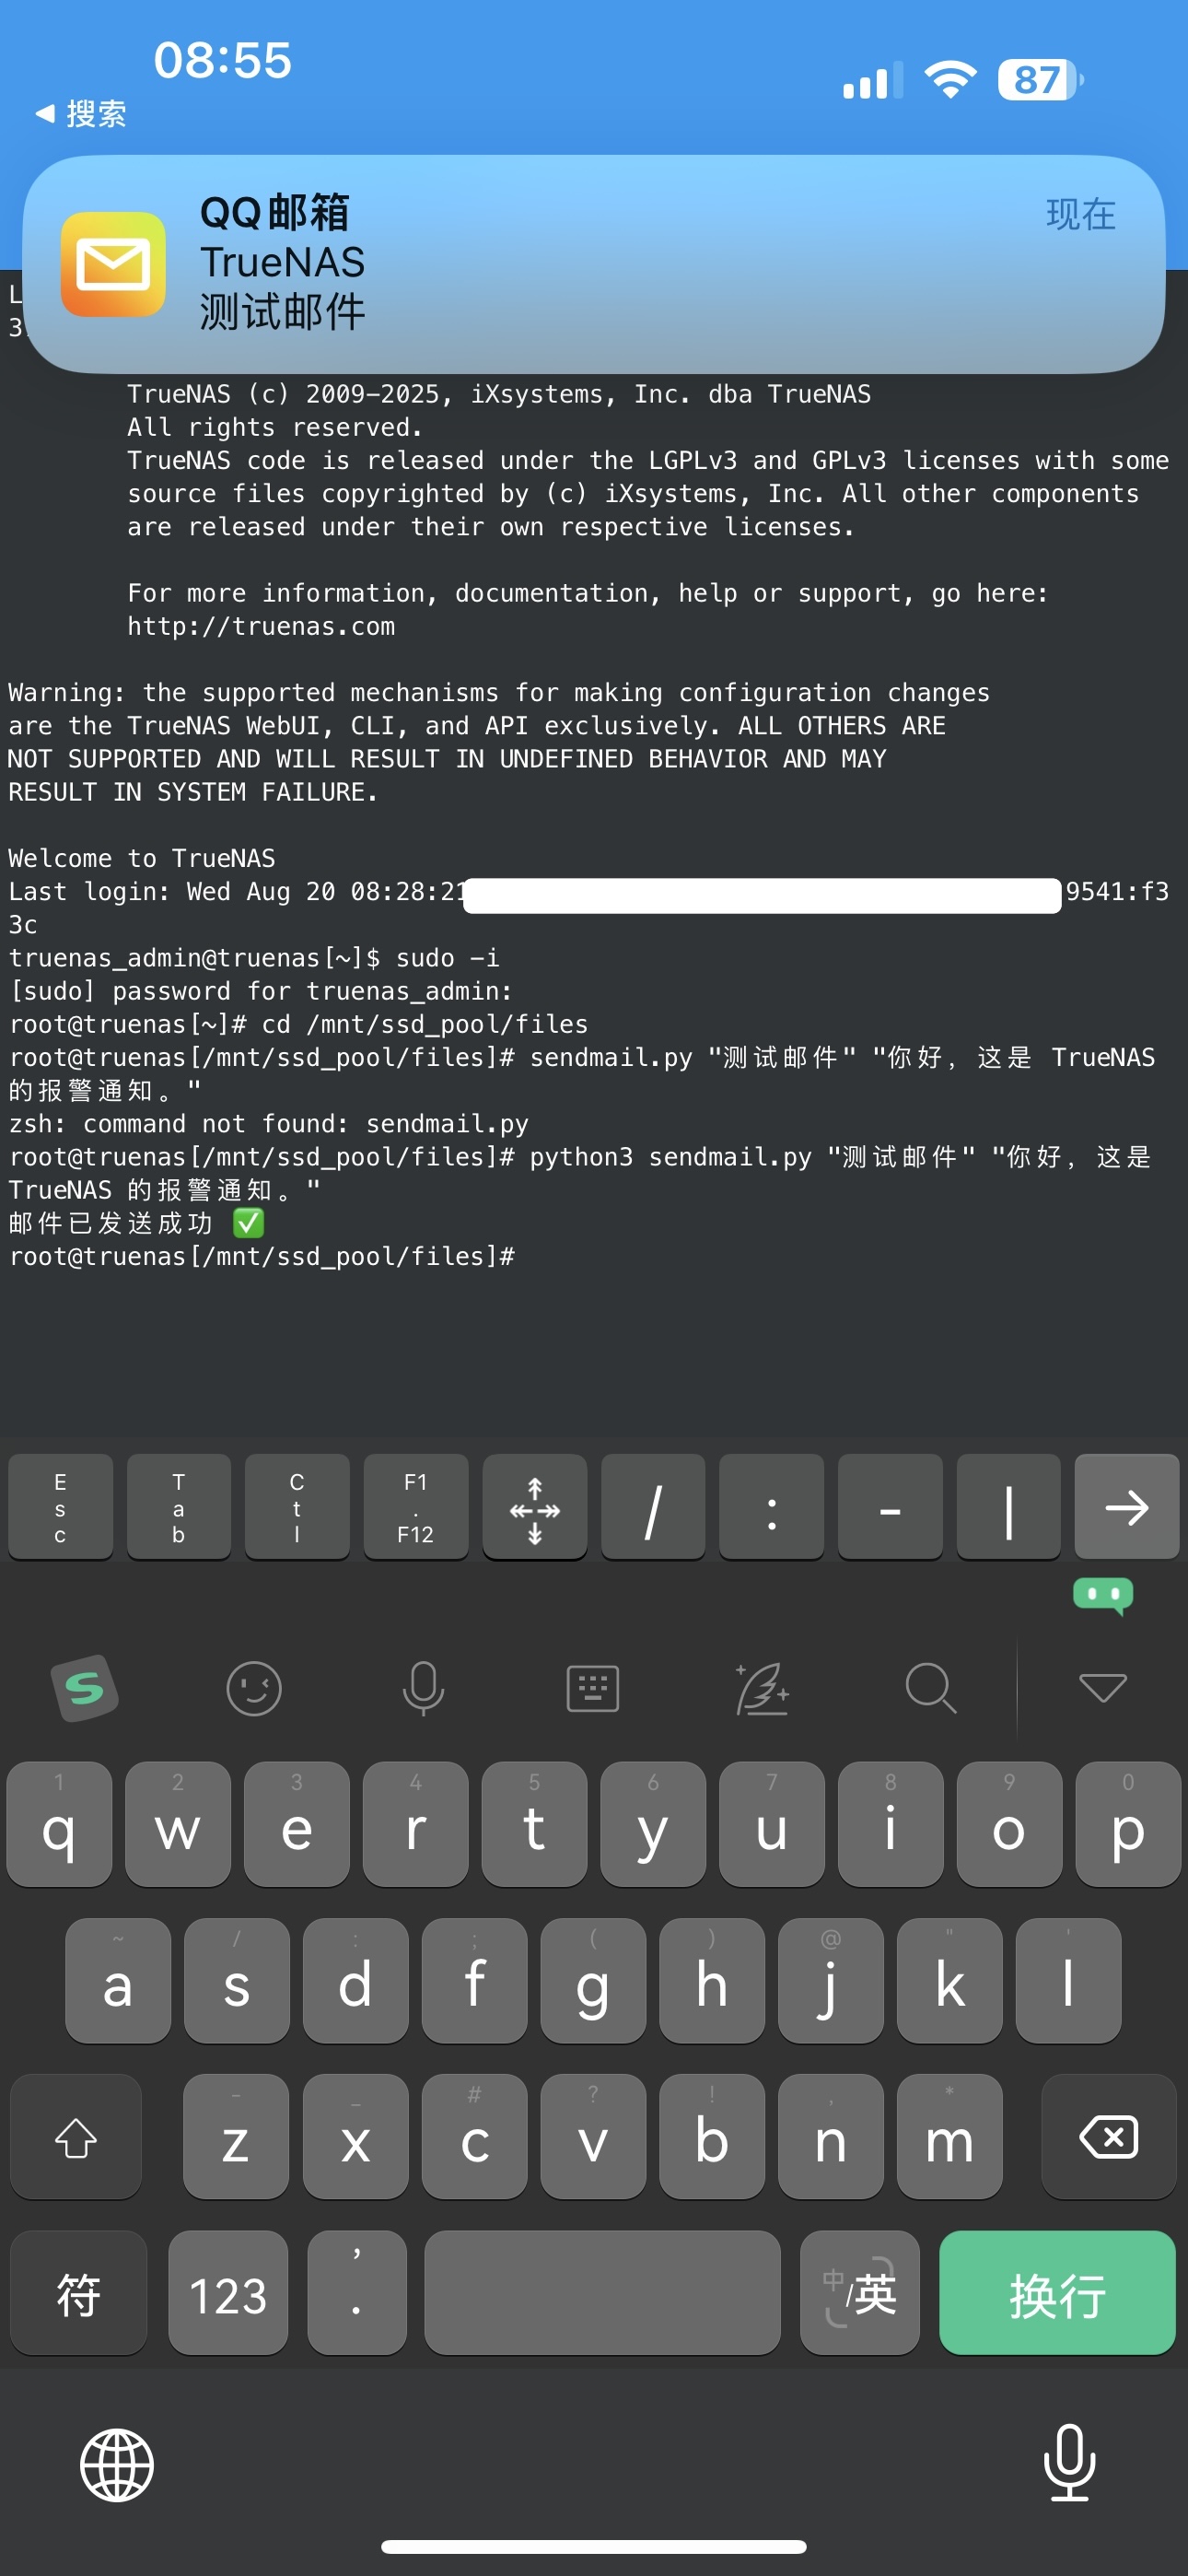
I use QQ mailbox to send errors or even send more requests to add “server.quit()”, which is more stable
#!/usr/bin/env python3
配置
SMTP_SERVER = “smtp.qq.com ”
def send_mail(subject, content):
context = ssl.create_default_context()
try:
    server = smtplib.SMTP_SSL(SMTP_SERVER, SMTP_PORT, context=context)
    server.login(SENDER, PASSWORD)
    server.sendmail(SENDER, [RECEIVER], msg.as_string())
    server.quit()  # 显式关闭连接,Linux 下更稳定
    print("邮件已发送成功 ✅")
except Exception as e:
    print("发送邮件失败 ❌:", e)
if name == “main ”:
oxyde
August 20, 2025, 3:55am
2
opened 12:37PM - 25 Jun 25 UTC
closed 04:46PM - 29 Jun 25 UTC
Original link: https://github.com/JoeSchmuck/Multi-Report/issues/27
**Backgrou… nd**:
- I'm using QQ SMTP service and configured correctly in TrueNAS's Email Settings.
- Try running mr_sendmail v.0.17 or v1.11 manually but found error.
**Issues**:
1. Mail from address must be the same as authorization user
2. Run mr_sendmail and end up with an error message, but the email is received. Error is “KO: (-1, b'\x00\x00\x00')”
**Error msg**:
```bash
{"error": true, "detail": "KO: (501, b'Mail from address must be same as authorization user.', 'TrueNAS@local.com')", "logfile": null, "total_attach": 0, "ok_attach": 0}
```
```bash
python3 mr_sendemail-v1.11.py --debug_enabled --subject "TEST $(date)" --to_address "ABC@qq.com" --mail_body_html " Test Content $(date)"
Security Advice: The current user (UID=0) is not the owner of the directory '/mnt/MediaFiles/Backup/Scripts' (Owner UID=3000).
{"error": true, "detail": "KO: (-1, b'\\x00\\x00\\x00')", "logfile": "/mnt/MediaFiles/Backup/Scripts/sendemail_log/20250625_094021.txt", "total_attach": 0, "ok_attach": 0}
```
<details><summary>The sendemail_log</summary>
<p>
File sendemail_log/20250625_094021.txt successfully generated
18 totals file log
0 totals attachment to handle
trying read mail.config
read mail.config successfully
Switching for the right provider
** SMTP Version **
From found
parsing smtp config
switch from classic send and bulk email
mail hmtl provided
parsing html content
no file found, plain text/html output
start parsing headers
parsing data from config and override options
using mr-config fromname-email
generate a message ID using ABC@qq.com
domain: qq.com
uuid: 2025_06_25_09_40_21_8003bfdb822-c881-4bff-8b79-8bbd26300e08
messageid: <2025_06_25_09_40_21_8003bfdb822-c881-4bff-8b79-8bbd26300e08@qq.com>
check for attachements...
get hostname
hostname retrieved: TrueNAS.local
tryng retrieving if more recipient are set
establing connection based on security level set on TN: SSL
entered SSL path
adding ehlo to the message
entering credentials
sending SSL email
KO: (-1, b'\x00\x00\x00')
</p>
</details>
**How to Fix**:
1. Pretty easy, just update "multi_report_config.txt" and ensure "**From=**" config is same as "**Email=**"
```bash
###### Email Address(s)
### Enter your Email address to send the report to. To send to multiple email addresses separate those using a semicolon ";".
### The from address does not need to be changed unless you experience an error sending the email, however some email servers
### only use the email address associated with the email server so you may need to add your email address for the server in use.
Email="ABC@qq.com" # Send normal emails to this address
From="ABC@qq.com" # From address (default works for many)
```
2. Has to change/enhance the Python script to handle the error; here is the fix.
https://github.com/JoeSchmuck/Multi-Report/blob/db7b59fb0a7cc2a719d034975ec5ed5a38930517/mr_sendemail.py#L381-L391
To
```python
elif smtp_security == "SSL":
mail_sent_successfully = False
send_result = None
try:
with smtplib.SMTP_SSL(smtp_server, smtp_port) as server:
append_log(f"entered {smtp_security} path")
if hostname:
append_log("adding ehlo to the message")
server.ehlo(hostname)
if smtp_login:
append_log("entering credentials")
server.login(smtp_user, smtp_password)
append_log(f"sending {smtp_security} email")
# Key changed: save sendmail results
send_result = server.sendmail(smtp_senderemail, to_address, msg.as_string())
mail_sent_successfully = True
append_log(f"Sendmail completed, result: {send_result}")
# check results
if not send_result:
append_log("All recipients processed successfully")
else:
failed_recipients = list(send_result.keys())
append_log(f"Some recipients failed: {failed_recipients}")
except Exception as ssl_error:
error_str = str(ssl_error)
append_log(f"Exception during SMTP: {ssl_error}")
# If mail is sent successfully, but has a connection error will be ignored
if mail_sent_successfully and any(indicator in error_str for indicator in [
'(-1,', 'connection', 'reset', 'closed', 'broken pipe'
]):
append_log("Connection ended after successful send - treating as success")
else:
process_output(True, f"KO: {ssl_error}", 1)
```
**Expected results:**
- The output: "error": true → "error": false"
```bash
python3 mr_sendemail-v1.1test.py --debug_enabled --subject "TEST $(date)" --to_address "ABC@qq.com" --mail_body_html "Test Content $(date)"
Security Advice: The current user (UID=0) is not the owner of the directory '/mnt/MediaFiles/Backup/Scripts' (Owner UID=3000).
{"error": false, "detail": "<< Email Sent >>Security Advice: The current user (UID=0) is not the owner of the directory '/mnt/MediaFiles/Backup/Scripts' (Owner UID=3000).", "logfile": "/mnt/MediaFiles/Backup/Scripts/sendemail_log/20250625_101628.txt", "total_attach": 0, "ok_attach": 0}
```
- "KO: (-1, b'\\x00\\x00\\x00')" → "<< Email Sent >>"
<details><summary>sendemail_log</summary>
<p>
cat sendemail_log/20250625_101628.txt
File sendemail_log/20250625_101628.txt successfully generated
20 totals file log
0 totals attachment to handle
trying read mail.config
read mail.config successfully
Switching for the right provider
** SMTP Version **
From found
parsing smtp config
switch from classic send and bulk email
mail hmtl provided
parsing html content
no file found, plain text/html output
start parsing headers
parsing data from config and override options
using mr-config fromname-email
generate a message ID using ABC@qq.com
domain: qq.com
uuid: 2025_06_25_10_16_28_760082b090b-a263-450c-9b3a-2e1c4b80bc09
messageid: <2025_06_25_10_16_28_760082b090b-a263-450c-9b3a-2e1c4b80bc09@qq.com>
check for attachements...
get hostname
hostname retrieved: TrueNAS.local
tryng retrieving if more recipient are set
establing connection based on security level set on TN: SSL
entered SSL path
adding ehlo to the message
entering credentials
sending SSL email
Sendmail completed, result: {}
All recipients processed successfully
Exception during SMTP: (-1, b'\x00\x00\x00')
Connection ended after successful send - treating as success
Email Sent via SMTP
<< Email Sent >>Security Advice: The current user (UID=0) is not the owner of the directory '/mnt/MediaFiles/Backup/Scripts' (Owner UID=3000).
</p>
</details>
Here you find some info and how i handle this QQmail “problem” in my sendemail (basically i have to ignore those kind of exception).
S_R
August 20, 2025, 4:20am
4
smtp.send_message(msg)
Just add quit
oxyde
August 20, 2025, 5:26am
5
In my script i have used the context manager sintax
with smtplib.SMTP_SSL(..., timeout=30) as server:
that should implicitly send the server.quit command, but i get reported that the same exception where raised anyway, and this happening only with QQmail.
context = ssl.create_default_context()
But i need to look into that deeper to avoid regressions, but hey, you give me a really good point to start